
Security
Nodana's protected hosting combines a fixed host image, signed node software, encrypted wallet storage and verifiable boot measurements. These protections reduce the access needed to operate your node and let compatible clients check the host and node software before trusting them with sensitive information.
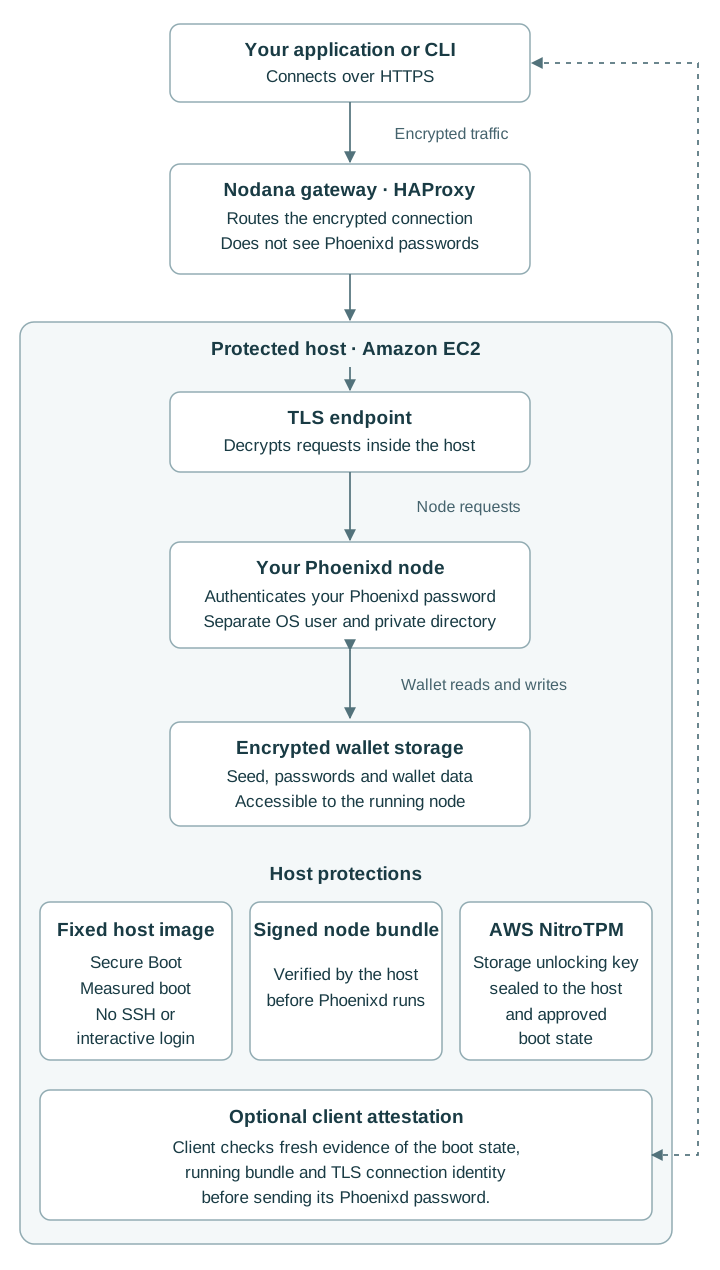
Protected hosts
Phoenixd runs on Amazon EC2 hosts configured with Secure Boot and AWS NitroTPM. Secure Boot restricts which boot image can run. NitroTPM records measurements of the boot software and configuration, and protects the key used to unlock wallet storage.
The host boots a fixed image containing the operating system and the controller that manages nodes. It has no SSH access or interactive console login. Changing the operating system or controller requires a replacement host image.
Phoenixd, its runtime libraries and its launcher form a separately signed Nodana bundle. The host verifies the bundle before running it. Node software can be updated separately from the host image, using the node's existing wallet data.
Each node runs under a separate operating-system user with its own private data directory and Phoenixd passwords. Nodes can share a protected host; each node is not a separate virtual machine.
Encrypted wallet storage
Wallet data is stored on an encrypted volume. Its unlocking key is sealed to the host's NitroTPM and measured boot state. Copying the volume to another instance, or booting different software, does not by itself provide access to that key.
The approved host software unlocks the volume to run Phoenixd. Encryption protects stored data; the running software still needs access to wallet data to process payments.
Your credentials
Nodana generates your node's recovery seed and Phoenixd passwords during creation and sends them to the protected host over an authenticated, encrypted connection. The dashboard shows these credentials from the creation response over HTTPS while your node launches.
Save your credentials when they are shown. The API does not store them in the account database, and the dashboard does not save them in browser storage. Phoenixd retains the wallet seed and passwords on the protected host to operate your node.
Save the credentials and recovery material provided during setup somewhere secure. Keep recovery material separate from the application that uses your node.
Use the limited password for reading node information and creating invoices. The full password also permits spending and closing channels. Anyone with the full password can control funds through the node's API. See API authentication for connection examples.
Nodana's management service authenticates separately to protected hosts to create, start, stop and delete nodes. Your Phoenixd passwords grant access to your node's API; they do not grant access to host management.
Encrypted connections
Applications connect to your node over HTTPS. Our HAProxy gateway routes the encrypted connection to the protected host. TLS is terminated inside that protected host, where Phoenixd access is authenticated. HAProxy does not decrypt application requests or receive their passwords, and the TLS private key remains inside the protected hosts.
The proxy limits new connections and simultaneous connections from each client IP address before forwarding traffic to protected hosts. These limits help protect nodes from connection floods and excessive reconnecting. Applications sharing a public IP address share those limits. Reuse connections where supported and back off before reconnecting if a connection is refused.
Attestation
Attestation lets you check your node's host and software using fresh, AWS-signed evidence tied to its HTTPS connection.
Use the CLI attestation command with your node's URL and a host release checksum, a node bundle checksum, or both. Supply both to approve the exact host and bundle releases; with only a bundle checksum, the CLI uses Nodana's signed host approvals. The CLI reference explains how to obtain the checksums and read the result. No Phoenixd password or Nodana account login is required.
A successful check confirms that the evidence is valid and the supplied checksums match. You still trust the approved software, your client and AWS's Nitro infrastructure; attestation does not guarantee that the software is free of vulnerabilities or that a running process has never been compromised.
Protect your account and recovery material
- Enable two-factor authentication on your Nodana account.
- Keep passwords and access keys in trusted secret storage. Do not put them in URLs, public repositories or support messages.
- Give applications limited access unless they need to spend funds.
- Keep your recovery material securely outside Nodana.
If you lose access to your node, use your recovery seed with another Phoenixd instance to recover your wallet. Existing channels are not preserved in this recovery flow.
If you suspect an account or credential has been compromised, contact us without including passwords, private keys or recovery words.